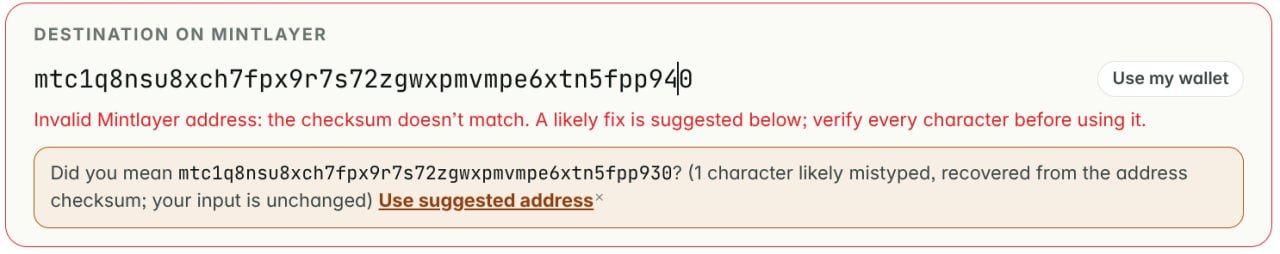
Someone sends funds to a Mintlayer address and mistypes one character. Look at the picture below: the software caught it.
It did more than refuse the input. It realised the address was invalid, realised the typo sits at the end of the string, a 40 where a 30 should be, and proposed the corrected address to the user. One click and the payment goes to the right place.
That behaviour is not a trick and not a lucky catch. It is a property of the address format itself, chosen before Mintlayer had a block explorer, a wallet, or a token.
Mintlayer uses bech32 addresses. The format carries a checksum computed over the whole string, which gives it two properties that sound small until you watch what happens without them.
First, errors are detected. Change, drop, or swap characters and the checksum breaks. The wallet knows the address is wrong before anything is signed.
Second, errors are locatable. Bech32 can pinpoint where the damage is, so the wallet can propose the corrected address instead of just saying "invalid" and leaving you to compare strings by eye.
Now the comparison nobody in this industry likes to make.
Most 0x chains use addresses that are raw hexadecimal. A checksum exists there too, but it is optional, encoded in letter casing, and frequently skipped by the very tools people trust. Many wallets accept whatever you paste without a sound.
Here is the part that should end the discussion: on these chains, virtually every lowercase string is a valid address. Not "valid and somebody's." Just valid. A typo produces a well-formed address that belongs to no one, has never belonged to anyone, and never will. The funds arrive at a coordinate in a 160-bit space where the only other visitor is the arithmetic that generated it.
The industry even gave the phenomenon a monument. The zero address, 0x000...0, has absorbed millions of dollars in tokens sent there by mistake or on purpose, unrecoverable by construction. Entire websites track the graveyard. The error mode is so well known that burning funds has become a feature.
The standard answer to all of this is "verify it yourself, character by character." Your bank does not ask you to proofread your IBAN. Your email client does not ask you to validate an MX record. Payments infrastructure asking users to be their own checksum is not security, it is the absence of it.
This is what security by design means in practice. Not a bug bounty page, not an audit sticker, not a blog post after an incident. The decision was made at the protocol level, years ago, in the choice of an address format that makes entire classes of user error impossible instead of probable.
Mintlayer has been in production for years, holding real funds, on an address format that was right the day we picked it. Security is not the feature you add when the product is finished. It is the reason the product looks the way it does from the first commit.